


AI and infrastructure news
Filter by type: All68
HPAC-IDS: intrusion detection with hierarchical attention
An article published on January 14, 2025 describes a method that analyzes network-packet segments and reports promising results on CIC-IDS2017.
- 17 days ago jhalon.github.io
V8 Internals: Browser Security in Focus
Published on April 20, 2025, the article opens a three-part series on Chrome internals and browser exploitation, introducing V8 and JavaScript internals.
- 17 days ago github.com
Fast response to compromised crypto wallets
Published on October 16, 2024, the text describes an open-source Bash script for attempting to recover funds from compromised wallets before bots move them.
- 18 days ago blog.quarkslab.com
Black-box analysis of Xiaomi’s MJA1 secure chip
On June 28, 2026, Quarkslab described an analysis of the MJA1 chip covering hardware, I2C traffic, flash extraction and firmware. The work mapped the command protocol and assessed security properties.
Practical attacks on privacy and availability in 4G/LTE networks
A 2015 article examines practical attacks affecting privacy and availability in 4G/LTE mobile communication systems.
- 18 days ago eprint.iacr.org
Secure backups for high-value secret keys
An article published on September 24, 2026, discusses backing up high-value secret keys and identifies their protection as a security concern.
- 18 days ago vercel.com
Benchmark compares models for vulnerability discovery
Published on July 18, 2026, the DeepSec benchmark compares model recall, precision, and cost in an open-core application for security analysis.
- 18 days ago bschaatsbergen.com
TPM-protected TLS client keys in Go
An article dated September 7, 2026 explains how to use a client certificate in Go whose private key remains in a TPM, and discusses the per-handshake performance cost.
- 18 days ago usenix.org
Study reports code overlap in network filtering systems
A USENIX Security paper reports code overlap between leaked Geedge Networks code and China's Great Firewall, including DNS and RST packet injection.
ExploitGym evaluates AI agents on vulnerability exploitation
The ExploitGym research proposes evaluating whether AI agents can turn vulnerabilities into impacts such as unauthorized file access or code execution.
Prompt injection in AI-analyzed binaries
Research from the Naval Postgraduate School, published on July 12, 2026, describes how strings in C binaries can influence language-model reverse-engineering agents.
- 18 days ago eeengineer.com
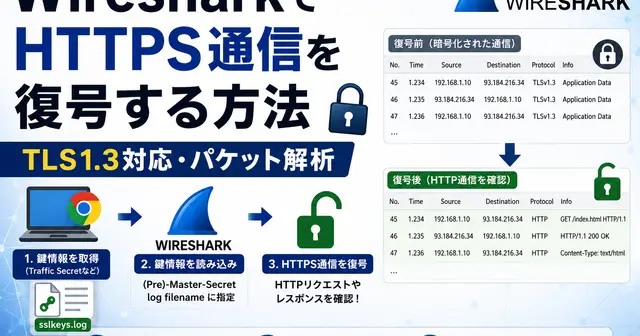
Authorized inspection of HTTPS traffic with TLS 1.3
An article published on August 29, 2026, explains how to record session secrets using SSLKEYLOGFILE and load them into Wireshark to inspect HTTP requests in captured HTTPS connections.
- 18 days ago cdrdv2-public.intel.com
Intel updates paper on memory protections
On July 1, 2026, Intel updated its technical paper on memory protections in Intel architecture for confidential computing, document 869103.
IO Factory and the detection of adaptive influence campaigns
An article published on August 12, 2026 describes an AI framework that simulates coordinated, adaptive campaigns and highlights the challenge of detecting this activity.
- 18 days ago github.com
Compile-time C obfuscation on Windows
The obfus.h repository describes a macro header for compile-time C obfuscation on Windows x86/x64 with tcc, including virtualization, anti-debugging, and control-flow obfuscation.
- 18 days ago hackers-arise.com
Research warns of cleartext traffic on GEO satellite links
Research published on June 18, 2026, reports that a significant portion of GEO satellite traffic is transmitted without encryption and could be intercepted using relatively accessible equipment.
Reverse-proxy phishing can bypass MFA
A post dated August 9, 2026, describes how phishing kits can relay logins and capture session cookies after multifactor authentication.
Device-code phishing is not limited to Wi-Fi
Published on July 25, 2026, the post warns that device-code authentication phishing can also occur over Ethernet or the internet.
- 18 days ago github.com
Post announces bootrom exploit for Apple chips
Published on June 18, 2026, the post says a bootrom exploit was released for A12, A13, S4/S5, and A12X/Z chips, which have not yet been tested.
- 18 days ago onejailbreak.com
Post reports decryption of protected iOS IPA without a physical iPhone
Published on September 27, 2026, the post claims that FairPlay-protected iOS IPAs can be decrypted without a physical iPhone or jailbreak. The report is relevant to app protection assessments.
- 18 days ago jeffgeerling.com
QuadRF tracks drones and detects Wi-Fi with a phased-array radio
In a post published on July 10, 2026, Jeff Geerling describes QuadRF, a radio built with a Raspberry Pi 5 and an FPGA board that uses signal processing and beamforming to track drones and detect Wi-Fi through walls.
- 18 days ago github.com
ARM repository offers 29 techniques for exploitation practice
Updated on June 28, 2026, the exploit_me repository provides a vulnerable ARM/AARCH64 application with 29 vulnerability techniques and obvious symbols removed for LLM fine-tuning experiments.
- 18 days ago github.com
Reversecore_MCP connects AI agents to reverse engineering
The GitHub repository describes an MCP server for AI agents that integrates binary-analysis tools and lists uses in reverse engineering, malware analysis, forensics, vulnerability research, and SAST.
- 18 days ago riotgames.com
Riot announces on-demand Vanguard operation
In a post published on June 24, 2026, Riot announced that Vanguard can run only during gameplay when specified device security features are enabled.
Windows tokens and privilege escalation risks
Published on June 27, 2026, the text explains how the Windows kernel’s _TOKEN structure represents identity and security attributes, and how token replacement has historically been used to gain SYSTEM privileges.
- 18 days ago tradecraftgarden.org
Tradecraft Garden presents a tool for testing evasion and detection
On June 30, 2026, Tradecraft Garden published a post about Crystal Palace, a linker that transforms and randomizes code, generates YARA rules, and supports reusable tradecraft modules.
uv can block malicious packages before installation
A note dated July 17, 2026, says setting UV_MALWARE_CHECK=1 makes uv query OSV before installing packages from remote registries and block those reported as malware.
- 18 days ago vulhunt.re
VulHunt: detecting vulnerabilities in binaries
In posts published on June 29, 2026, Binarly’s research team presents the VulHunt framework and an example detecting remote code execution in rsync.
 arxiv.org
Let's assess your project

I reply with scope and a proposal.