


Google FLARE's free guide teaches malware analysis from x86 assembly basics
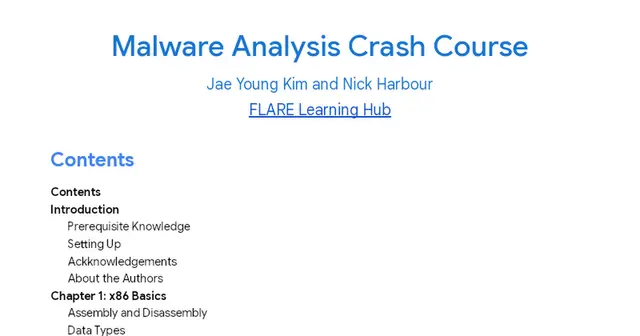
Free guide by Jae Young Kim and Nick Harbour of the FLARE Learning Hub structures malware analysis study from x86 assembly fundamentals through basic instruction concepts.
By Wendelmaques Pereira · Updated today
Source: Documento Malware Analysis Crash Course da Google FLARE (docs.google.com). Text prepared with AI from this source.
What happened and what to do
The guide Malware Analysis Crash Course, published as a Google Docs document by Jae Young Kim and Nick Harbour of the FLARE Learning Hub, is a free and structured resource for learning malware analysis. According to its preview, the chapters begin with x86 basics and run through instruction basics, meaning the fundamentals of assembly instructions.
For a company, the material can serve as a foundation for training internal security analysts or incident response teams. In practice, the work could include setting up a training path built on these chapters, an isolated lab for running samples safely, and records that track exercises and results. Analysis examples could also feed incident monitoring dashboards, without automating decisions that still require human judgment.
How the consultancy can help
Assessment of the team's malware analysis skills and incident response workflow; design and rollout of a study path with an isolated lab on the client's own infrastructure; operation with exercise tracking and progress indicators.
Next step
Send a short description of your case, such as the size of your security team and how incident response works today, and receive a scoped proposal with the project steps.
Let's assess your project

I reply with scope and a proposal.